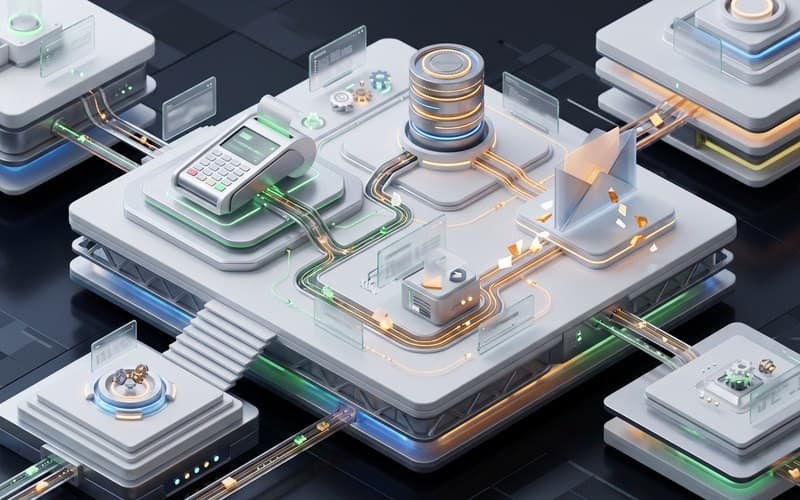
An Auth0 access and session audit dashboard gives security reviewers and tenant administrators real-time visibility into active user sessions, permission changes, and authentication anomalies. By unifying identity events and session controls into a centralised interface, engineering teams can inspect tenant boundaries, verify sign-ins, and invalidate compromised credentials immediately across web and mobile applications.
At Canvas Developers, our engineers build specialised identity consoles and enterprise audit workflows. This walkthrough details the screen hierarchy, streaming data flows, and acceptance safeguards required to build a resilient session audit dashboard powered by an enterprise Auth0 integration.
What Is the Purpose of an Auth0 Access and Session Audit Dashboard?
An Auth0 access and session audit dashboard serves as an operational control plane for enterprise identity management, giving engineering and compliance teams unified visibility across distributed applications. While Auth0 manages authentication protocols and tokens, organizations require custom audit consoles to enforce strict tenant isolation, monitor session lifecycles, and provide verifiable trails for regulatory frameworks like SOC 2 and ISO 27001.
The core record within this dashboard is the identity and session event, tying authentication tokens, IP addresses, user agents, and authorization grants to a specific session identifier. The system addresses three primary user roles with distinct operational requirements:
- End Users: View their personal active sessions across devices and initiate self-service revocation when an unrecognized device appears.
- Tenant Administrators: Audit team-level logins, track role assignments, inspect permission modifications, and terminate sessions across their specific tenant boundary.
- Security Reviewers: Perform forensic analysis across all tenants, correlate failed authentication spikes with potential credential stuffing, and verify compliance through tamper-evident logs.
By connecting an Auth0 integration to a dedicated presentation layer, teams decouple sensitive credential handling from analytical reporting while maintaining least-privilege administrative access.
What Screens, Role Interactions, and Error States Are Required?
Effective access and session audit dashboard development centers on providing operational clarity without exposing administrative interfaces to accidental token leakage or state confusion. A coherent screen hierarchy enables security personnel to transition smoothly from fleet-wide metrics to single-event inspections.
Core Views: Active Sessions, Permission Timeline, and Event Drilldown
The user interface organizes audit telemetry into three coordinated primary screens:
- Active-Session Overview: Displays real-time concurrent sessions aggregated by user and tenant. Each record displays client IP, geographic location, device fingerprint, and idle duration. Administrators can trigger session termination directly from this view, while end users access a scoped view restricted to their own devices.
- Permission-Change Timeline: Provides an immutable chronological audit trail tracking role bindings, permission grants, and scope changes. Entries highlight the initiating principal, target entity, timestamp, and previous versus updated state to simplify compliance reporting.
- Audit-Event Drilldown: A contextual drawer enabling security reviewers to inspect full event payloads. It correlates the session identifier with upstream authentication events, MFA challenges, and Management API calls without exposing raw tokens.
Resilient State Handling: Empty Views, Token Expiration, and API Failures
Robust Auth0 development demands rigorous defensive UI engineering across edge conditions. When tenants have no active sessions or filter criteria yield zero matches, empty states provide informative prompts rather than blank data grids.
For authentication lifecycles, the dashboard handles Management API token expiration through automated Machine-to-Machine token refresh loops before requests fail. If upstream rate limits occur (such as Auth0 api_limit thresholds) or network connectivity degrades, the interface implements exponential backoff with jitter, displays localized non-blocking error banners, and presents cached read-only data to maintain operational continuity.
How Does Data Flow Securely from Auth0 to the Audit Dashboard?
Architecting an enterprise identity pipeline requires decoupling live authentication flows from analytical query workloads. A production-ready Auth0 integration streams event telemetry into an intermediary ingestion service that indexes session activity while enforcing data hygiene.
Tracing Verified Sign-Ins, Permission Updates, and Revocations
Telemetry begins when an identity action executes within Auth0. The authentication engine generates event records categorized by official Auth0 Log Event Type Codes, such as s for successful logins, seacft for code exchanges, and sapi for Management API calls. Our ingestion worker captures these events via near-real-time Log Streams or webhooks, mapping them directly to identity records.
When an administrator revokes a session or updates role permissions, the event pipeline writes a timestamped ledger entry. Every aggregate metric on the dashboard links directly to these underlying source events, providing security reviewers with verifiable audit paths from user sign-in through credential termination.
Enforcing Tenant Isolation and Redacting Sensitive Credentials
Multi-tenant environments require strict logical isolation to prevent cross-tenant data exposure. When processing Auth0 tenant audit logs, our backend enforces organization-scoped filtering at both the API and database levels, ensuring administrators query only data corresponding to their authenticated organization identifier (org_id).
Furthermore, credential sanitization runs as an inline pipeline filter. Sensitive payloads, including authorization codes, refresh tokens, bearer tokens, and client secrets, are stripped or cryptographically hashed before writing to persistent storage. This ensures compliance with zero-trust principles and guarantees that audit logs remain safe for forensic review without exposing actionable authentication credentials.
How Do You Validate Session Revocations and Accelerate Delivery with AI?
Executing an accurate session revocation audit requires validating that terminating an active session invalidates associated credentials across both identity providers and client applications. Under official Auth0 Session Management API specifications, calling POST /api/v2/sessions/{id}/revoke revokes the session alongside all associated refresh tokens, whereas a standard DELETE call leaves refresh tokens active. Our acceptance tests assert that revoked sessions update their status in the UI immediately, associated refresh tokens fail on subsequent exchange, and OIDC Back-Channel Logout signals propagate to registered clients.
To accelerate implementation, our engineers leverage Auth0 vibe coding workflows using AI coding agents to generate UI components, schema definitions, and mock event fixtures. This automation shortens feedback loops during early scaffolding and interface prototyping. However, AI generators frequently miss edge cases such as token revocation race conditions, multi-tenant boundary checks, and asynchronous API retry semantics.
At Canvas Developers, experienced engineers direct the AI harness, review all code, and mandate rigorous automated test suites. We verify that logs redact sensitive tokens, validate rate-limiting middleware, and verify cryptographic signatures on log streams before production deployment.
How Should You Scope and Plan an Auth0 Audit Dashboard Project?
Planning successful Auth0 development begins by evaluating organizational compliance requirements against architectural complexity. For simple single-tenant applications with standard retention needs, Auth0's native dashboard viewer often suffices. However, when businesses require multi-tenant boundary isolation, delegated tenant administration, and immediate cross-client session revocation, developing a dedicated Auth0 access and session audit dashboard becomes essential.
Canvas Developers delivers production-grade identity solutions through structured scoping, milestone-based engineering, and comprehensive release testing. Depending on infrastructure governance, teams can choose between our Private/Local AI Engineering or commercial AI coding workflows directed by senior engineers. To discuss your authentication architecture, data constraints, and compliance objectives, submit your project details through our contact page to begin a scoped technical assessment.
Outcome
The architecture provides unified visibility into identity events and establishes verifiable audit paths from user sign-in through credential termination without exposing raw authentication tokens.